RBI cyber rules for payment operators: one rulebook, small firms by 2028
 By Neha KapoorEconomy Correspondent, Peepals Business
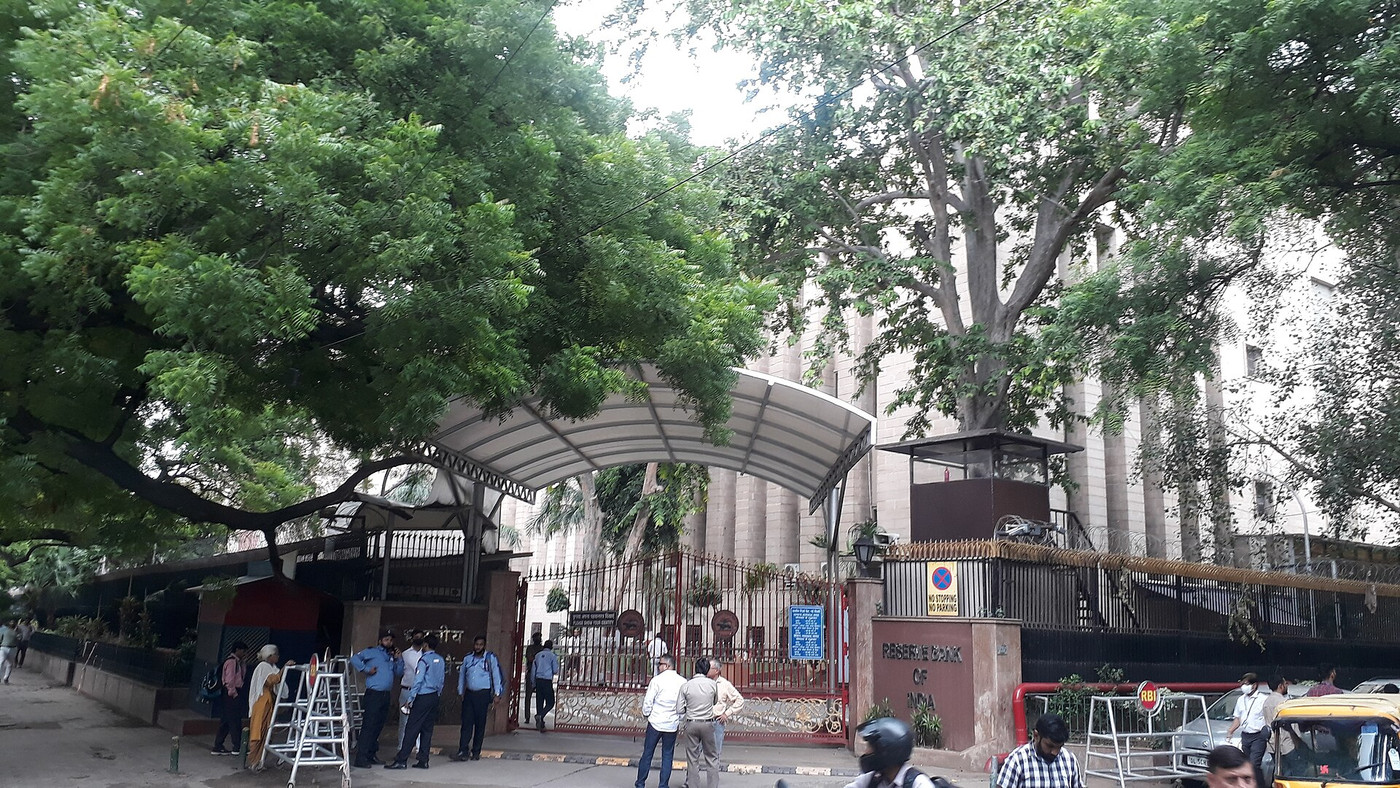
File photo: Pinakpani (CC BY-SA 4.0), via Wikimedia Commons
RBI's 5 November 2026 Master Directions merge cyber security rules for non-bank payment operators; large and medium firms comply now, small ones by 1 April 2028.
What Happened
The Reserve Bank of India (RBI) on Thursday, 5 November 2026 issued consolidated Master Directions on Cyber Resilience and Digital Payment Security Controls for non-bank payment system operators (PSOs), the companies outside the banking system that run India's card networks, payment gateways, prepaid wallets and white-label ATMs. The directions bring the RBI's July 2024 cyber security rules together with older instructions on system audits and on third-party ATM switch providers, and repeal six earlier circulars dating back to 2009. Large and medium operators must comply from the date of issue, while small operators have until 1 April 2028, according to reports of the directions.
Key Facts
- Issued: 5 November 2026, as Master Directions for authorised non-bank PSOs.
- Covered entities include payment aggregators, prepaid payment instrument (PPI) issuers such as wallet companies, card networks and white-label ATM operators (ATMs run by non-banks).
- Compliance: large and medium PSOs from the date the directions were placed on the RBI website; small PSOs by 1 April 2028.
- System audits: PSOs must submit an annual system audit report within two months of the end of their financial year, and their boards must review audit findings and compliance status.
- ATM switches: operators must make their third-party ATM switch providers (the companies whose systems route ATM transactions) follow the cyber security rules through their contracts, including blocking remote connections from outside machines to the switch network and preventing unauthorised backdoor access.
- Incident reporting: reports of the directions describe a six-hour window for reporting cyber attacks and critical outages to the RBI, with cyber incidents also reported to CERT-In, India's national cyber security agency.
- Six older circulars, the earliest from 2009, are repealed and replaced by the single framework.
Why It Matters
Many everyday digital payments in India pass through companies that are not banks: the payment gateway behind an online checkout, the wallet app on a phone, the card network that links a shop's terminal to a bank. A security failure at any one of them can stop payments for millions of people or expose card and account data. Until now the rules these companies had to follow were spread across several circulars written over 17 years. One rulebook makes it clearer what each operator must do, and easier for the RBI to check.
The ATM switch provisions address a specific weak point. Many white-label ATM operators and smaller payment firms rely on outside companies to run the switch, the system that passes a cash withdrawal request from the machine to the customer's bank. The new directions put responsibility on the operator to make those vendors meet the RBI's standards through binding contracts, rather than treating vendor security as someone else's problem.
For businesses, the main effect is cost and paperwork: board-level review of audits, tighter vendor contracts and fast incident reporting need staff and systems. For customers, the aim is fewer outages and fewer frauds that start with a weak link in the payment chain.
Peepals calculation: Small payment operators get 513 days to comply, from 5 November 2026 to 1 April 2028, or about 17 months (513 ÷ 30.4 ≈ 16.9), while large and medium operators had to comply from day one. The single rulebook replaces six circulars issued over roughly 17 years (2009 to 2026). Our calculation from the reported figures.
| Operator size | Must comply from |
|---|---|
| Large non-bank PSOs | 5 November 2026 (date of issue) |
| Medium non-bank PSOs | 5 November 2026 (date of issue) |
| Small non-bank PSOs | 1 April 2028 |
Impact
Short-term: Large and medium payment companies need to check their security controls, vendor contracts and incident reporting against the consolidated directions now.
Long-term: A single, stricter framework is likely to raise the cost of running a payment business, which may favour larger operators, while making the payment system harder to attack.
Who is affected: Payment aggregators, wallet and prepaid card issuers, card networks, white-label ATM operators, their technology vendors, and the customers who use digital payments.
What to watch next: The 1 April 2028 compliance deadline for small payment operators.
Key Takeaway
The RBI's 5 November 2026 Master Directions put all cyber security rules for non-bank payment operators in one rulebook, binding large and medium firms now and small firms from 1 April 2028.
Questions and Answers
What did the RBI issue on 5 November 2026?
Consolidated Master Directions on Cyber Resilience and Digital Payment Security Controls for non-bank payment system operators, combining the July 2024 rules with older audit and ATM switch instructions.
Which companies must follow the new RBI cyber security rules?
Authorised non-bank payment system operators, including payment aggregators, prepaid wallet issuers, card networks and white-label ATM operators.
When do small payment operators have to comply?
By 1 April 2028. Large and medium operators must comply from the date the directions were published.
Do the rules change anything for ordinary users?
Users do not have to do anything. The rules require payment companies to strengthen their own security, audit it every year and report attacks quickly, which is meant to reduce outages and fraud.
Disclaimer: Prepared by the Peepals newsroom from publicly available sources with AI assistance. Information is accurate to the best of our knowledge at the time of publication and may change. Images may be representative. Not professional advice. Report an error via our contact page.
By Neha Kapoor, Economy CorrespondentCovers Economy and more for Peepals Business. All stories by Neha Kapoor
Scripbox IPO step: turns public company after Rs 12.7 crore FY25 profit
Micron stock rebounds 5% after 17% crash on US data-centre fears
Get the day's stories in your inbox
Peepals Weekly: the week decoded, free. One email a week, unsubscribe in one click.
Neha Kapoor is a pen name of the Peepals Global Editorial Team, which researches, fact-checks and publishes every story. The portrait is an illustration.